अर्थव्यवस्था और साइबर सुरक्षा: संदिग्ध डेटा सेंधमारी के बीच SBI ने ग्राहकों को दिया सुरक्षित फंड का आश्वासन
24 Oct 2026
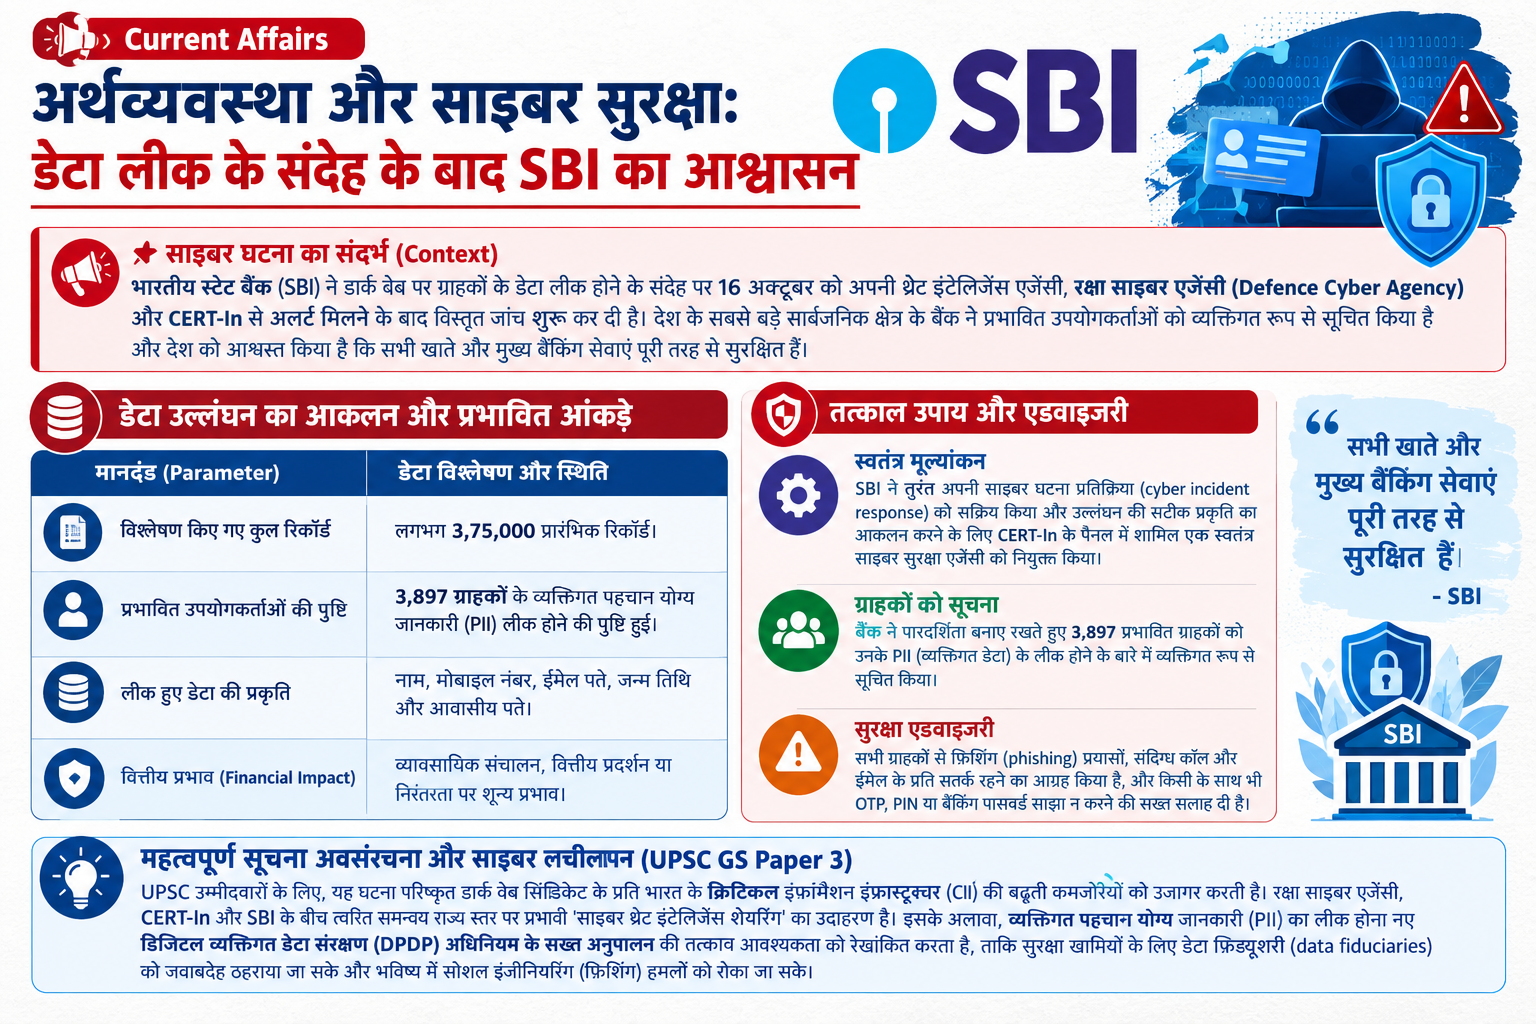
डार्क वेब पर डेटा लीक के संदेह के संबंध में CERT-In और रक्षा साइबर एजेंसी के अलर्ट के बाद, भारतीय स्टेट बैंक (SBI) ने ग्राहकों को आश्वस्त किया है कि उनका पैसा और मुख्य बैंकिंग सेवाएं पूरी तरह से सुरक्षित हैं।
भारतीय स्टेट बैंक (SBI) ने डार्क वेब पर ग्राहकों के डेटा लीक होने के संदेह पर 16 अक्टूबर को अपनी थ्रेट इंटेलिजेंस एजेंसी, रक्षा साइबर एजेंसी (Defence Cyber Agency) और CERT-In से अलर्ट मिलने के बाद विस्तृत जांच शुरू कर दी है। देश के सबसे बड़े सार्वजनिक क्षेत्र के बैंक ने प्रभावित उपयोगकर्ताओं को व्यक्तिगत रूप से सूचित किया है और देश को आश्वस्त किया है कि सभी खाते और मुख्य बैंकिंग सेवाएं पूरी तरह से सुरक्षित हैं।
| मानदंड (Parameter) | डेटा विश्लेषण और स्थिति |
|---|---|
| विश्लेषण किए गए कुल रिकॉर्ड | लगभग 3,75,000 प्रारंभिक रिकॉर्ड। |
| प्रभावित उपयोगकर्ताओं की पुष्टि | 3,897 ग्राहकों के व्यक्तिगत पहचान योग्य जानकारी (PII) लीक होने की पुष्टि हुई। |
| लीक हुए डेटा की प्रकृति | नाम, मोबाइल नंबर, ईमेल पते, जन्म तिथि और आवासीय पते। |
| वित्तीय प्रभाव (Financial Impact) | व्यावसायिक संचालन, वित्तीय प्रदर्शन या निरंतरता पर शून्य प्रभाव। |
- स्वतंत्र मूल्यांकन: SBI ने तुरंत अपनी साइबर घटना प्रतिक्रिया (cyber incident response) को सक्रिय किया और उल्लंघन की सटीक प्रकृति का आकलन करने के लिए CERT-In के पैनल में शामिल एक स्वतंत्र साइबर सुरक्षा एजेंसी को नियुक्त किया।
- ग्राहकों को सूचना: बैंक ने पारदर्शिता बनाए रखते हुए 3,897 प्रभावित ग्राहकों को उनके PII (व्यक्तिगत डेटा) के लीक होने के बारे में व्यक्तिगत रूप से सूचित किया।
- सुरक्षा एडवाइजरी: बैंक ने सभी ग्राहकों से फ़िशिंग (phishing) प्रयासों, संदिग्ध कॉल और ईमेल के प्रति सतर्क रहने का आग्रह किया है, और किसी के साथ भी OTP, PIN या बैंकिंग पासवर्ड साझा न करने की सख्त सलाह दी है।
UPSC उम्मीदवारों के लिए, यह घटना परिष्कृत डार्क वेब सिंडिकेट के प्रति भारत के क्रिटिकल इंफॉर्मेशन इंफ्रास्ट्रक्चर (CII) की बढ़ती कमजोरियों को उजागर करती है। रक्षा साइबर एजेंसी, CERT-In और SBI के बीच त्वरित समन्वय राज्य स्तर पर प्रभावी 'साइबर थ्रेट इंटेलिजेंस शेयरिंग' का उदाहरण है। इसके अलावा, व्यक्तिगत पहचान योग्य जानकारी (PII) का लीक होना नए डिजिटल व्यक्तिगत डेटा संरक्षण (DPDP) अधिनियम के सख्त अनुपालन की तत्काल आवश्यकता को रेखांकित करता है, ताकि सुरक्षा खामियों के लिए डेटा फिड्यूशरी (data fiduciaries) को जवाबदेह ठहराया जा सके और भविष्य में सोशल इंजीनियरिंग (फ़िशिंग) हमलों को रोका जा सके।
Economy & Cybersecurity: SBI Assures Safe Funds Amid Suspected Data Breach
24 Oct 2026
Following alerts from CERT-In and the Defence Cyber Agency regarding a suspected dark web data leak, the State Bank of India (SBI) has assured customers that their funds are completely secure and core banking operations remain unaffected.
The State Bank of India (SBI) initiated a rapid, detailed cybersecurity investigation after receiving critical alerts on October 16 from its Threat Intelligence Service Provider, the Defence Cyber Agency, and CERT-In regarding suspected customer data exposure on the dark web. The country’s largest public sector lender has individually notified affected users, assuring the nation that all account balances and core banking services remain entirely secure.
| Parameter | Data Analysis & Status |
|---|---|
| Total Records Analyzed | Approximately 3,75,000 preliminary records. |
| Confirmed Affected Users | 3,897 customer records confirmed to have Personally Identifiable Information (PII) exposed. |
| Nature of Exposed Data | Names, mobile numbers, email addresses, dates of birth, and residential addresses. |
| Financial Impact | Zero material impact on business operations, financial performance, or continuity. |
- Independent Assessment: SBI immediately activated its cyber incident response protocols and appointed an independent, CERT-In empanelled cybersecurity agency to establish the exact nature and extent of the breach.
- Customer Notification: Transparency was maintained by individually notifying the 3,897 affected customers about the exposure of their PII.
- Security Advisory: The bank strongly urged all customers to remain vigilant against phishing attempts, suspicious calls, and emails, strictly advising against sharing OTPs, PINs, or banking passwords.
For UPSC aspirants, this incident highlights the growing vulnerabilities of India's Critical Information Infrastructure (CII) to sophisticated dark web syndicates. The rapid coordination between the Defence Cyber Agency, CERT-In, and SBI exemplifies effective state-level cyber threat intelligence sharing. Furthermore, the exposure of Personally Identifiable Information (PII) underscores the urgent necessity for strict compliance with the newly enacted Digital Personal Data Protection (DPDP) Act to penalize data fiduciaries for security lapses and prevent subsequent social engineering (phishing) attacks.